Mantis features
Tools to deploy, control access, and analyze failures across your infrastructure.
Config-as-Code
Your deployments as typed, versioned Nickel
Deployment Automation
Versioned deployments with one-click rollback
Reliability & Scale
Designed to survive an execution server going offline
Multi-Tenancy
Tenant-scoped data isolation
Security & RBAC
Fine-grained access control with SSO
Connected Fleet
Onboard agents securely, run anywhere
AI-Powered Analytics
Log analysis for deployment failures
Integrations
Connect your existing tools
Your deployments as typed, versioned Nickel
Define your whole deployment surface as typed Nickel documents — actions (inline commands and storage-backed scripts), sequences, solutions, environments, variables, schedules, freezes, promotions, and notification channels. Keep them in Git and bidirectional sync holds Git and Mantis in lockstep, with an optional Git-authoritative mode that makes the repo the source of truth — and a secret-safe export that never leaks credential values.
- Actions as typed Nickel — inline commands and storage-backed scripts
- Sequences, solutions, environments, variables, schedules, freezes
- Bidirectional GitOps sync (push, pull, preview)
- Git-authoritative reconcile with managed-entity guards
- Secret-safe export — encrypted values never reach the repo
- Octopus Deploy converter: deployment processes and variables to Nickel

Versioned deployments with one-click rollback
Deploy solutions, sequences, or individual actions across distributed targets. Standard, rollback, point-in-time recovery, promotion, and redeployment patterns — with live, streamed progress.
- Solution, sequence, and action deployments
- Standard, rollback, and promotion patterns
- Point-in-time recovery with variable snapshots
- Parallel, sequential, and rolling execution modes
- Deployment freezes with admin overrides
- Scheduled and recurring deployments

Designed to survive an execution server going offline
A durable dispatch queue retries and ages out work, multiple execution servers share the load, and orphaned targets are reassigned automatically when a server goes offline — so deployments continue without operator action.
- Durable dispatch queue with retry and TTL
- Horizontal scale across execution servers
- Automatic target reassignment on failover
- Live 3D view of your control-plane topology
- Graceful shutdown and recovery
- Real-time status via server-sent events

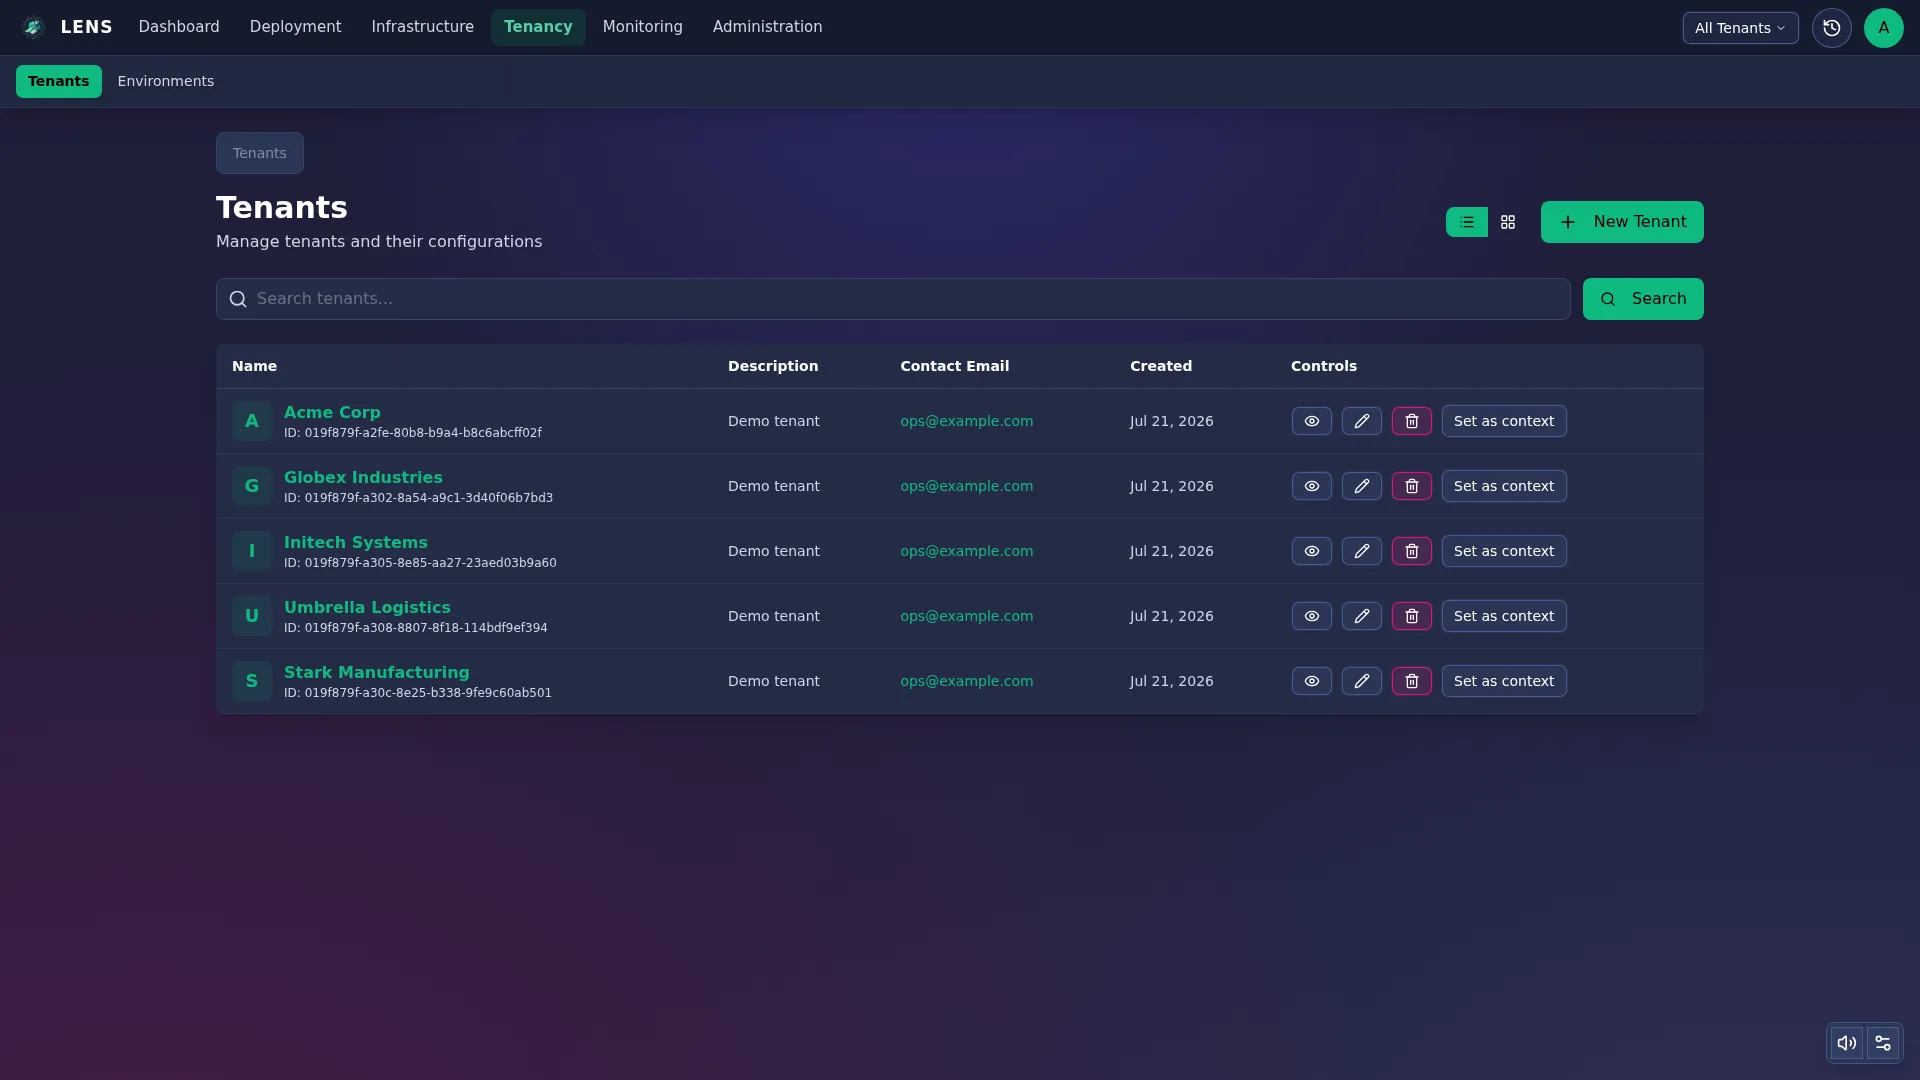
Tenant-scoped data isolation
Tenant data is isolated: deployment histories, variables, tags, and audit trails are scoped and filtered per tenant. Audit entries are hash-chained and blocked from update or unauthorized delete by database triggers.
- Tenant-scoped deployment data, variables, and tags
- Independent deployment histories
- Tenant-scoped variables and tags
- Hash-chained audit entries with per-tenant chain sequences
- Tenant-scoped access enforcement
- Tamper-evident audit trails
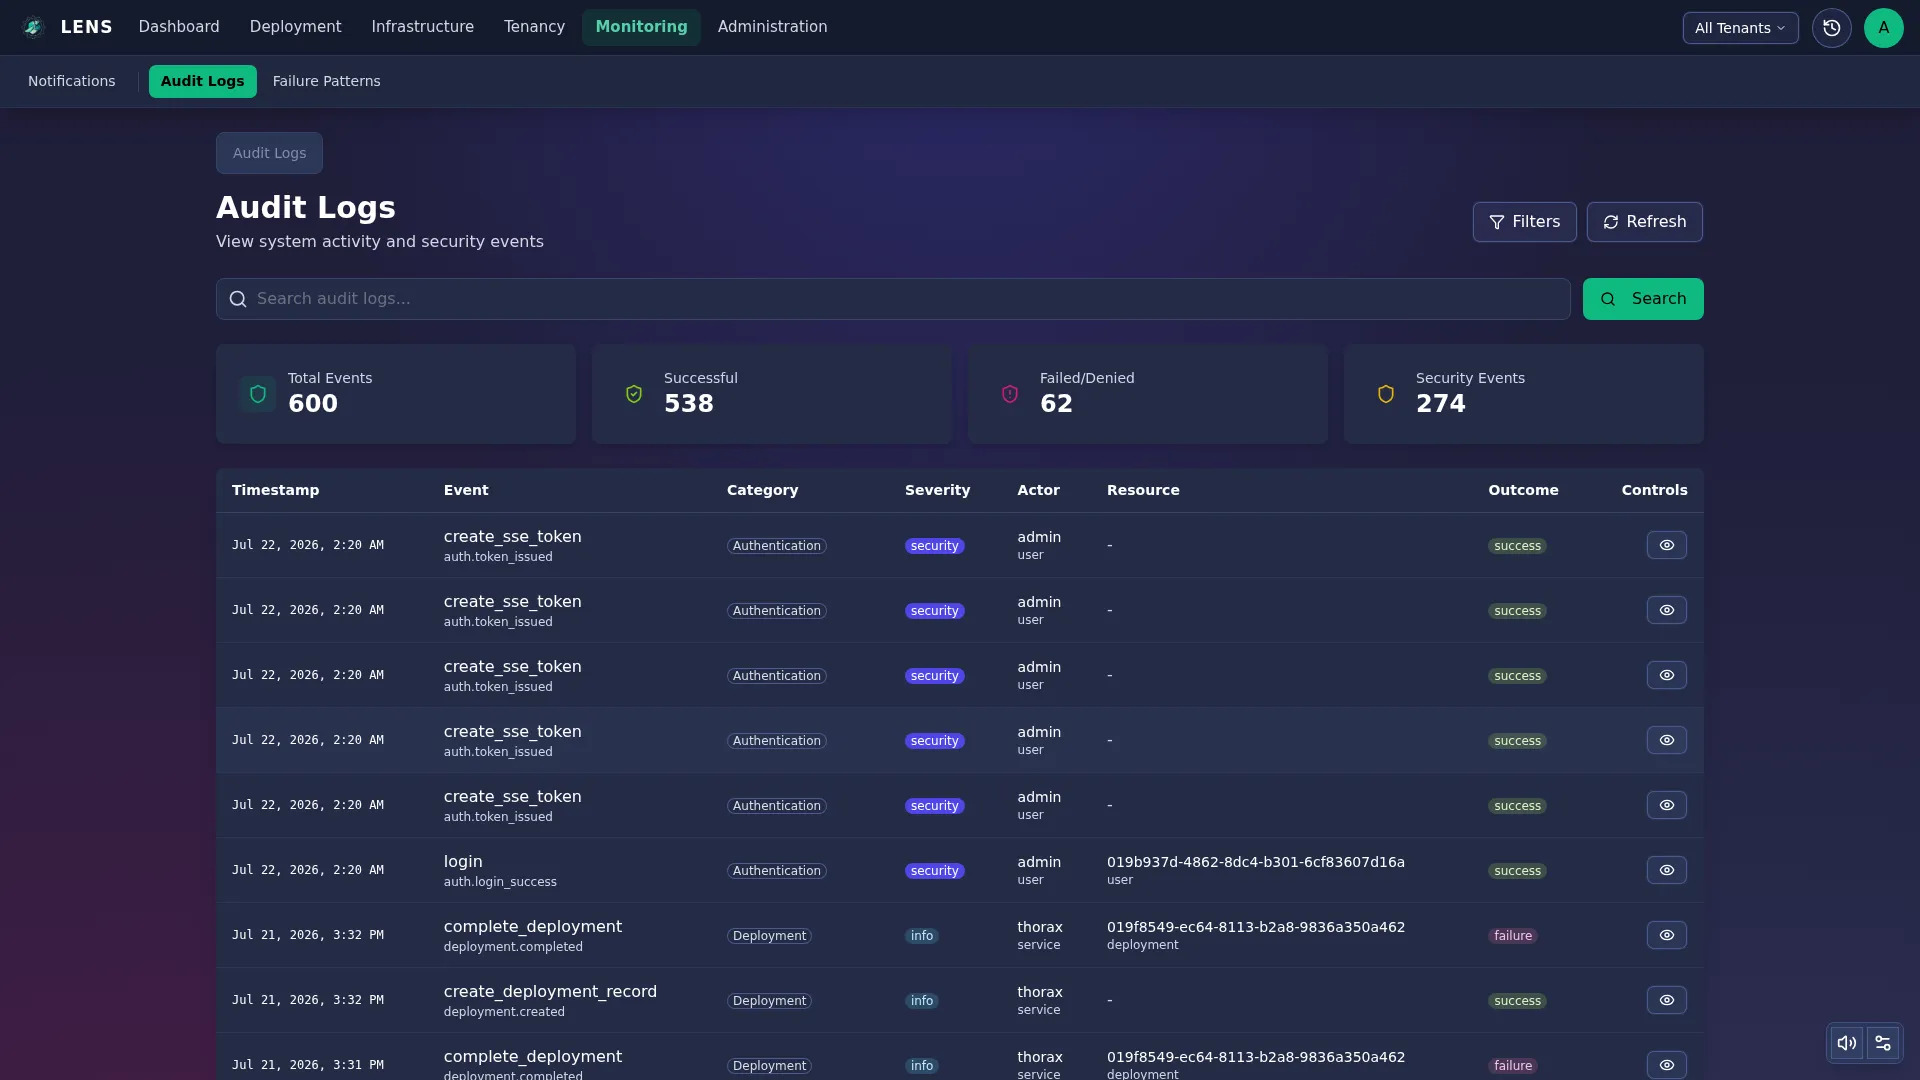
Fine-grained access control with SSO
Over a hundred resource-and-action permissions, OIDC single sign-on with any identity provider, and immutable cryptographic audit trails for compliance.
- Resource + Action permission model (100+ permissions)
- OIDC single sign-on
- Works with any OIDC provider; role sync from IdP groups
- Encryption of credentials at rest
- Immutable, hash-chained audit trails
- Tenant-scoped access enforcement
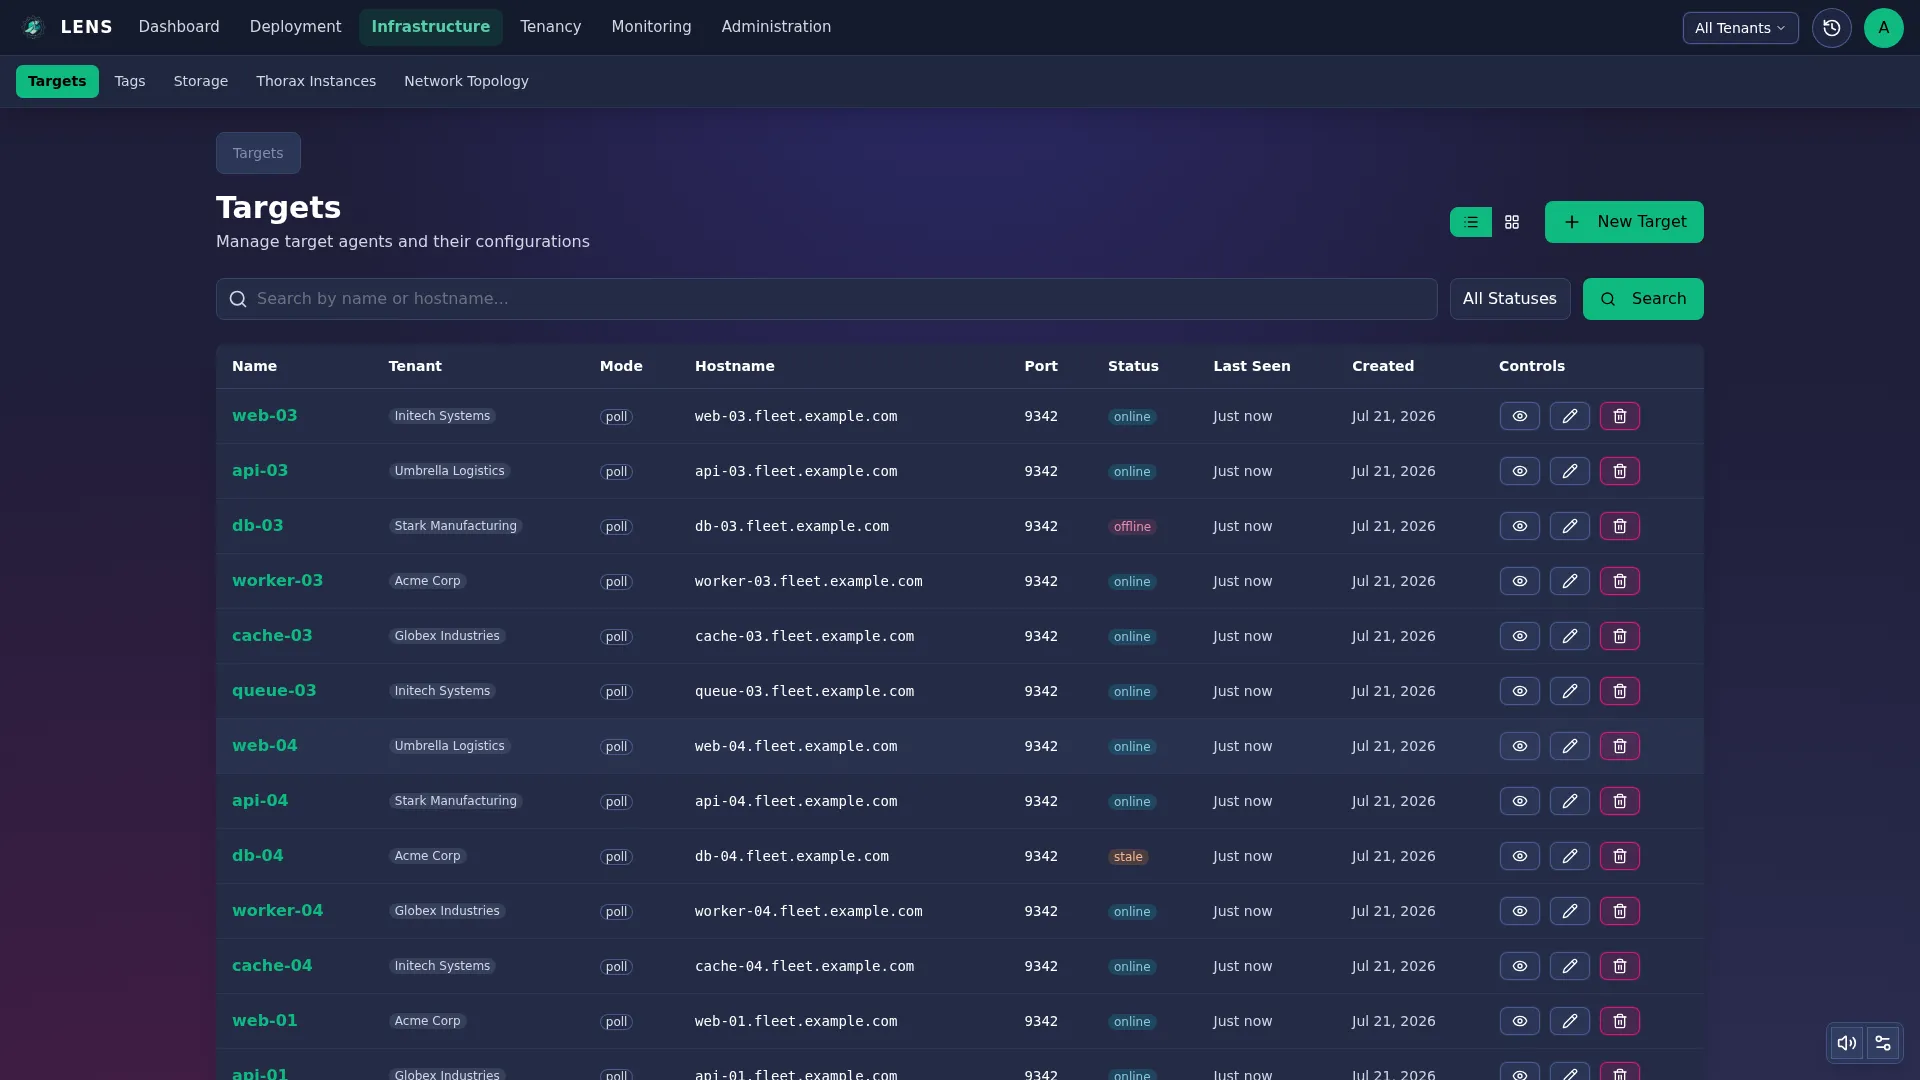
Onboard agents securely, run anywhere
Bring targets online with certificate-based agent enrollment — admin approval plus registration tokens you can scope with use limits and expiry (CA-signed CSR mode available). Push or pull execution runs shell and PowerShell scripts cross-platform, with optional WireGuard-based protected transport for NAT-traversed agents, layered under always-on mTLS.
- Certificate-based agent enrollment with admin approval
- Registration tokens with optional use limits, expiry, and auto-approve
- Listen (push) and poll (pull) execution modes
- sh, bash, zsh and PowerShell across Windows, Linux, macOS
- Target grouping via tags
- Optional WireGuard protected transport with NAT traversal
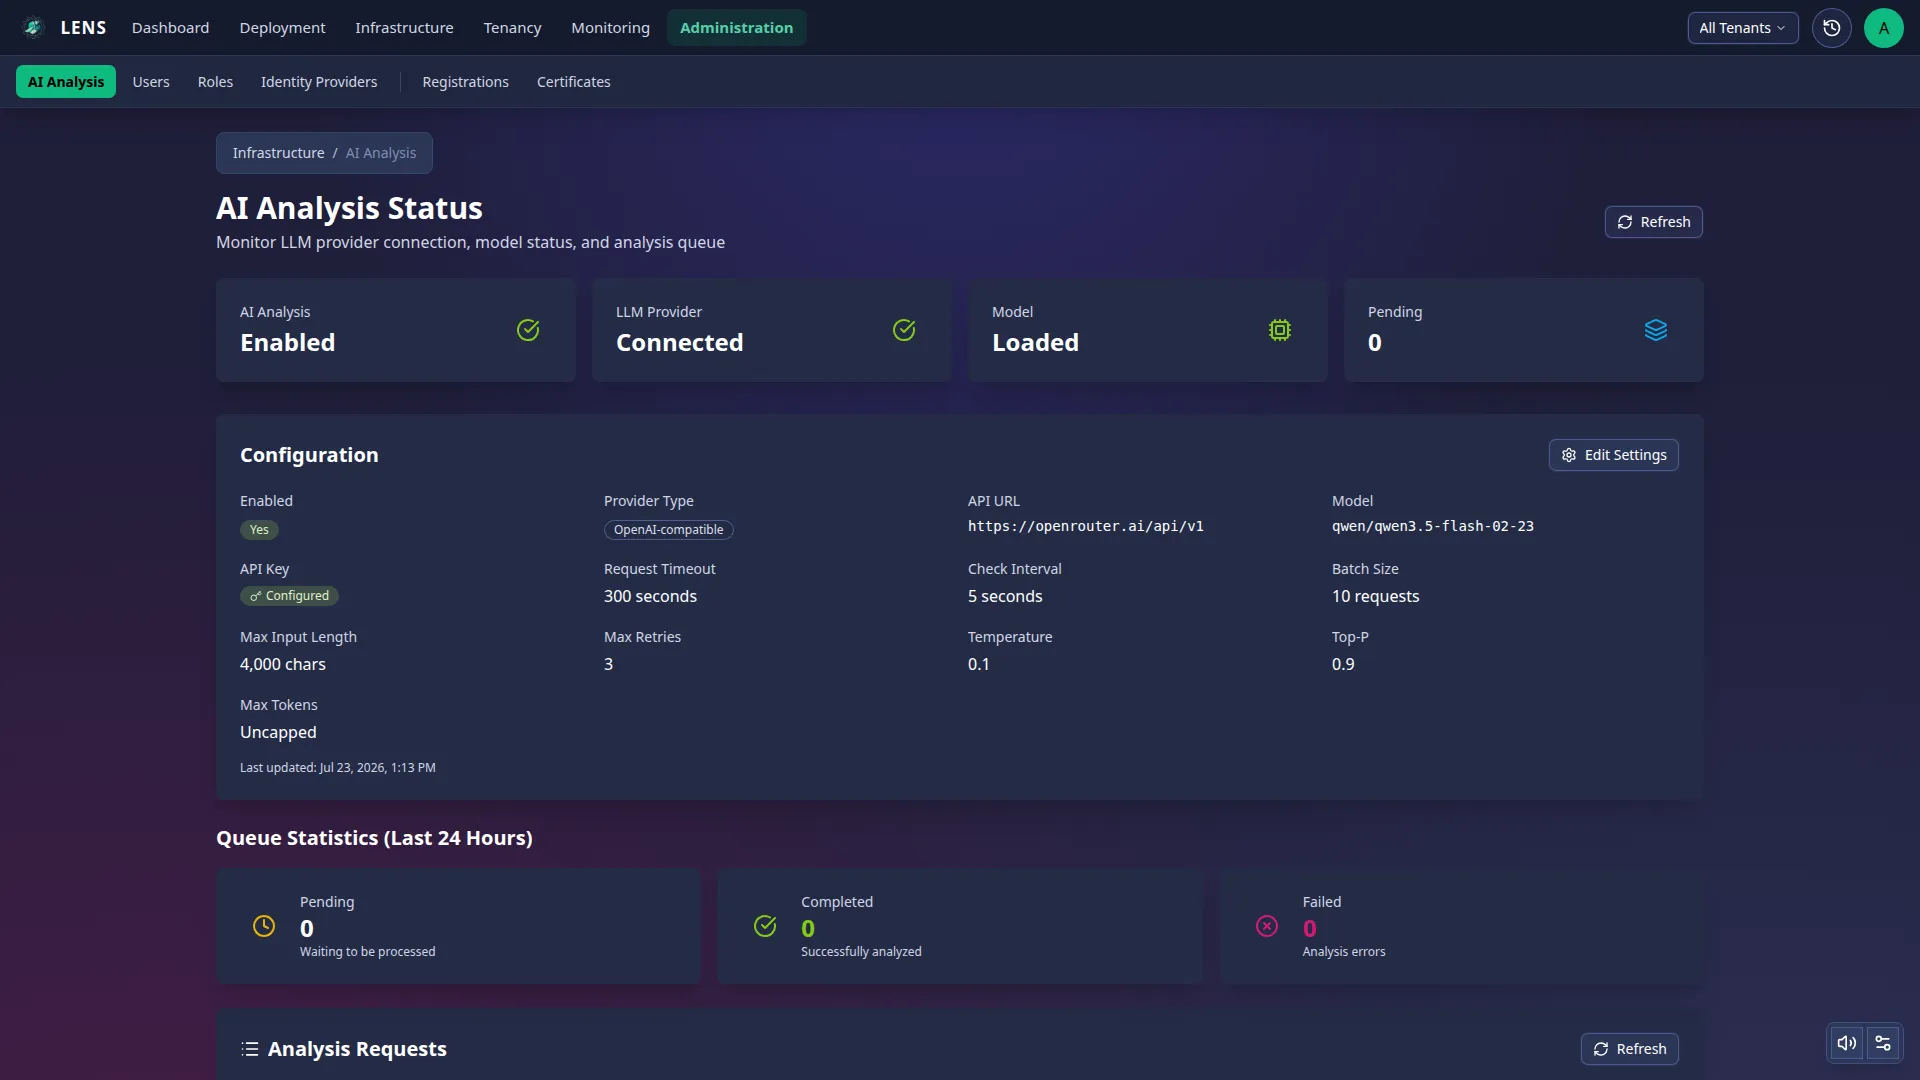
Log analysis for deployment failures
Opt-in deployment log analysis, via a configured LLM provider, detects patterns, identifies likely root causes, and suggests remediation with confidence scores.
- Error detection and classification
- Root cause analysis with confidence scores
- Remediation suggestions
- Pattern recognition across deployments
- Configurable analysis settings
- Batch processing for efficiency
Connect your existing tools
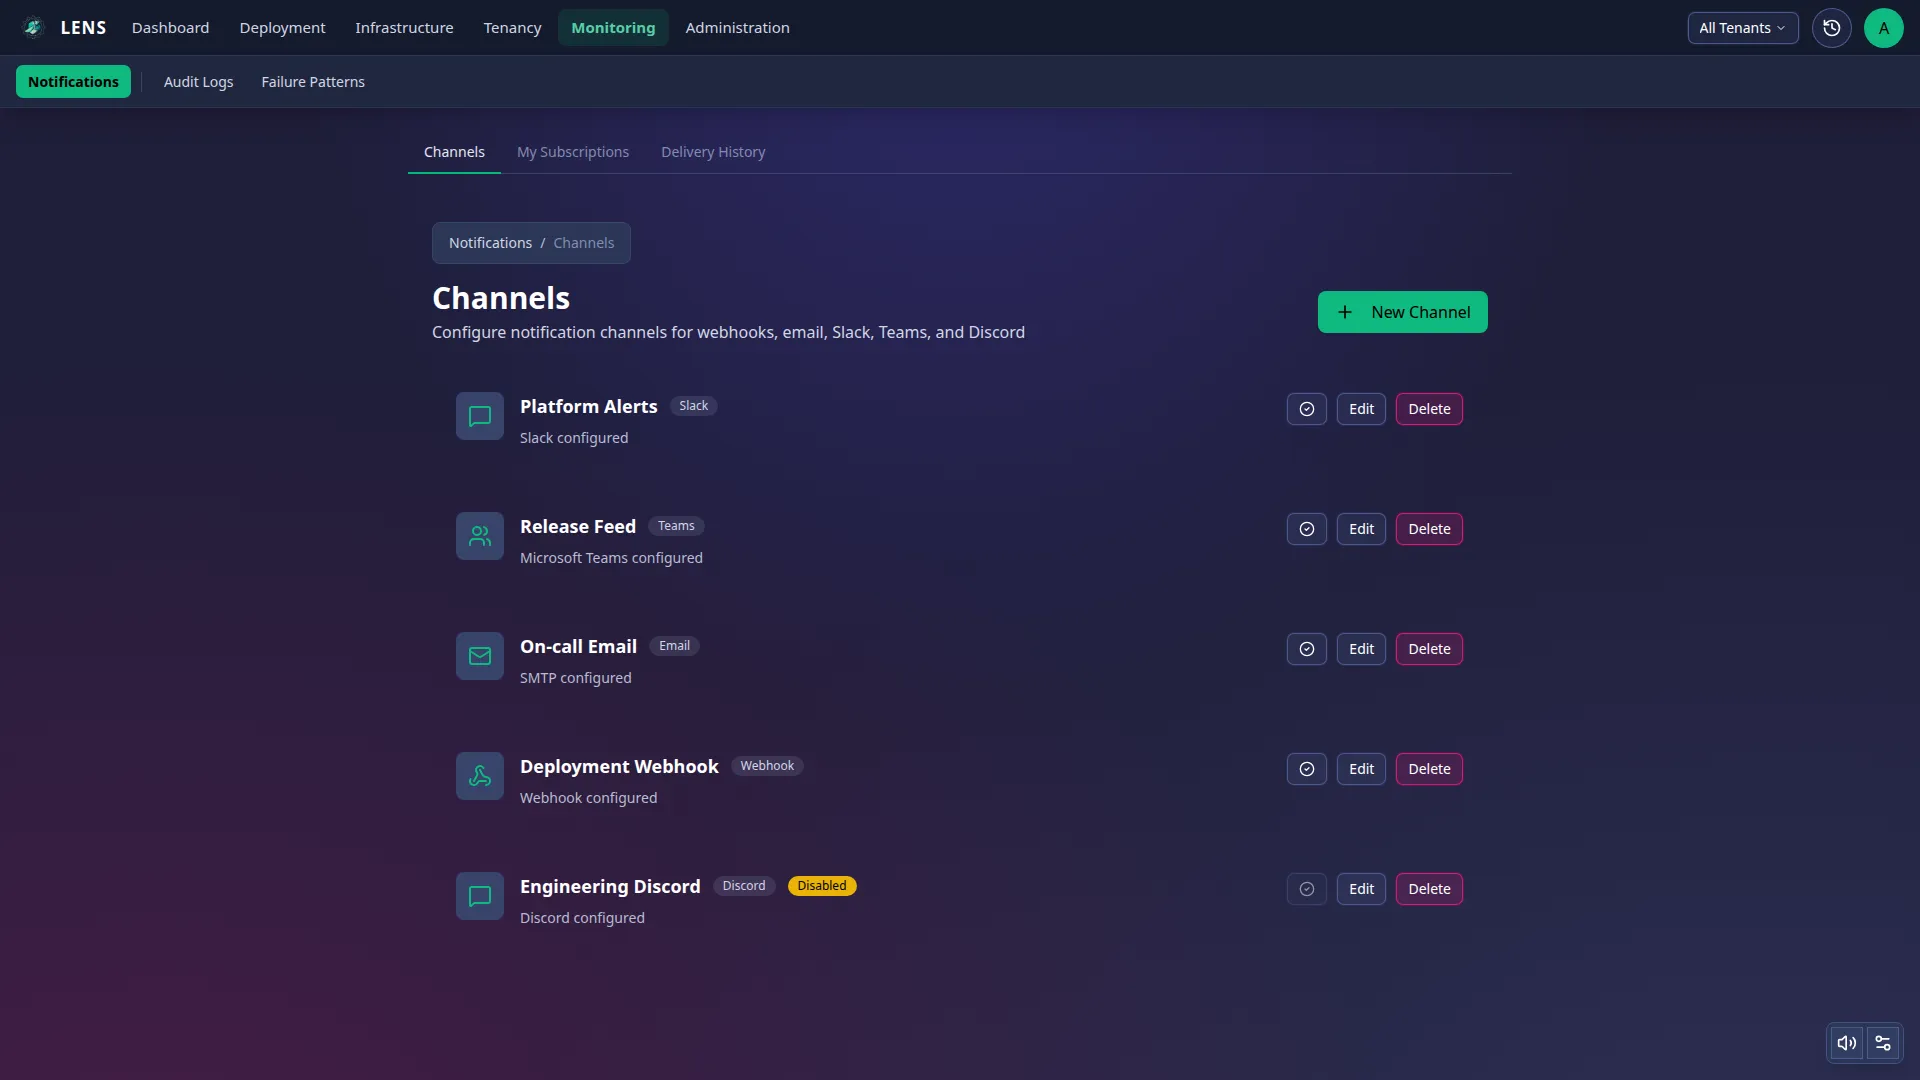
Notifications over email, Slack, Teams, Discord and signed webhooks, plus multiple storage backends. An API-first architecture for CI/CD integration.
- Email, Slack, Teams, Discord, and webhook notifications
- Git repository integration for scripts
- S3-compatible artifact storage
- HMAC-SHA256 signed webhooks
- Full REST API
- Server-sent events for real-time updates
Ready to try Mantis?
Deployment automation with version control, multi-tenant access control, and rollback. Self-hosted, free forever for personal, academic and nonprofit use.